01 · System DNS
Filter the traffic the PC relies on.
A local resolver checks destinations against current intelligence while allowed traffic continues to the network’s configured upstream resolver.


SafeLayer uses local-first filtering to block malicious domains, phishing infrastructure, and known command-and-control destinations across ordinary and encrypted browser paths.
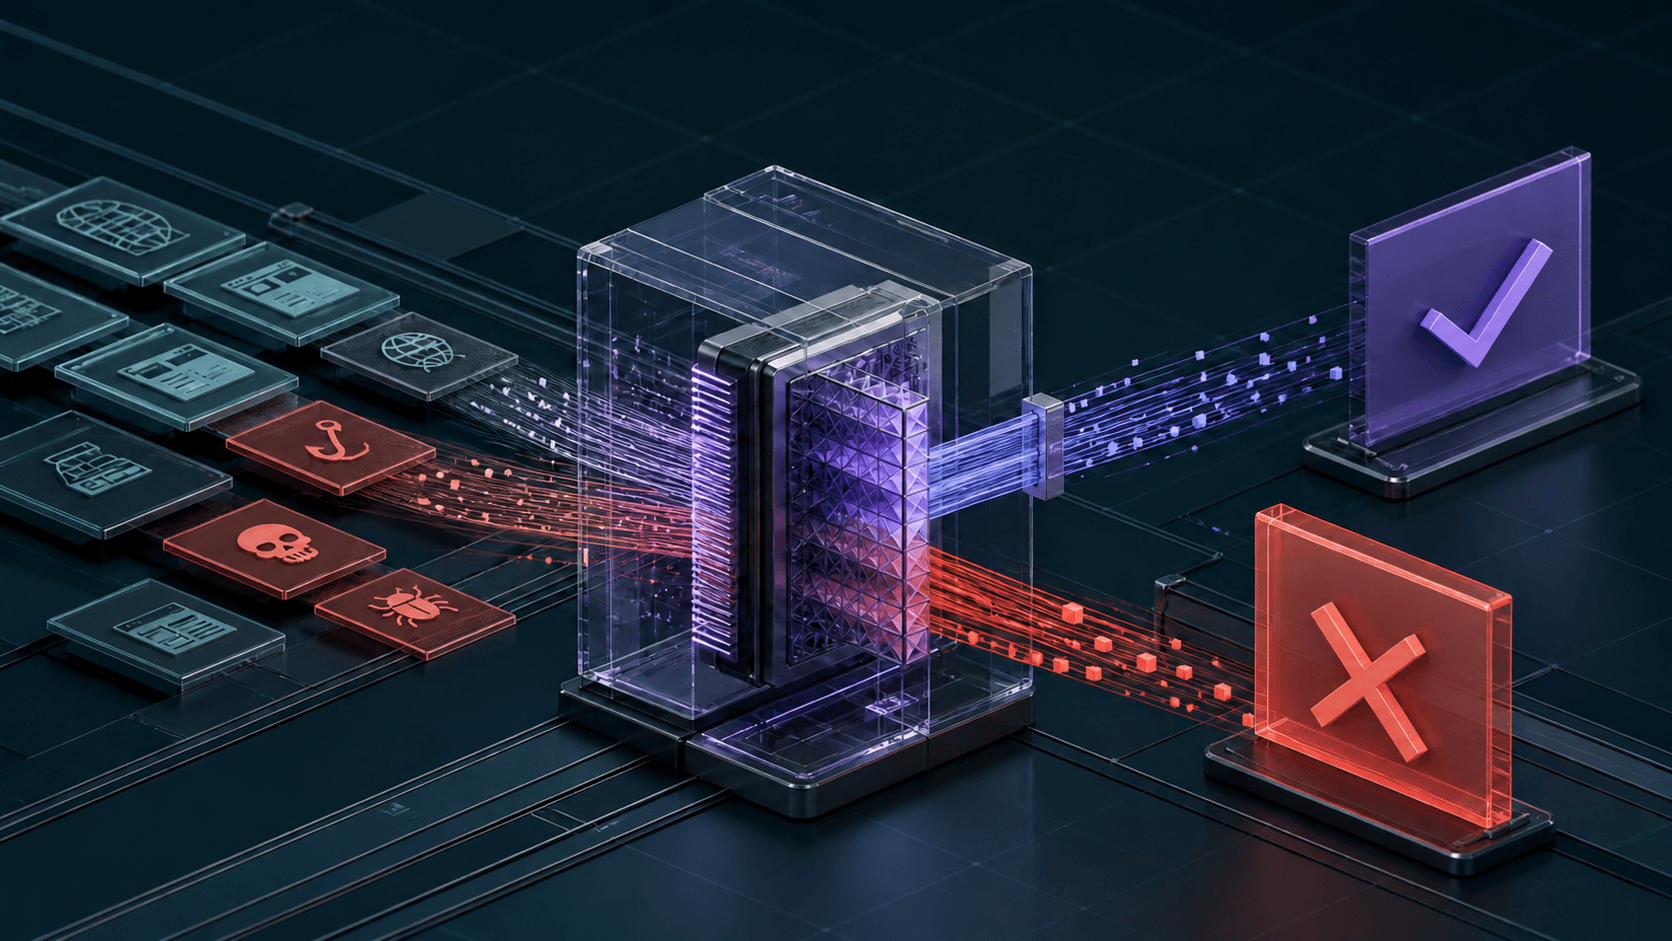
One local decision point
Ordinary system traffic and encrypted browser navigation share the same current threat intelligence.
One current blocklist
A browser can use its own encrypted DNS path and bypass a conventional system filter. SafeLayer keeps browser navigation and system DNS aligned with the same threat intelligence.
01 · System DNS
A local resolver checks destinations against current intelligence while allowed traffic continues to the network’s configured upstream resolver.
02 · Encrypted browser traffic
Browser navigation is checked before the page loads, so the same protection applies when encrypted DNS would otherwise bypass the system resolver.
03 · Safe operation
Capture-before-change safeguards, health checks, and a restore path make sure an unavailable filter does not leave the machine offline.
Protection that stays available
SafeLayer uses one local decision point for its domain intelligence, while independent safeguards keep normal browsing working when a dependency becomes unavailable.
Internet Protection